
Articles
Security
-
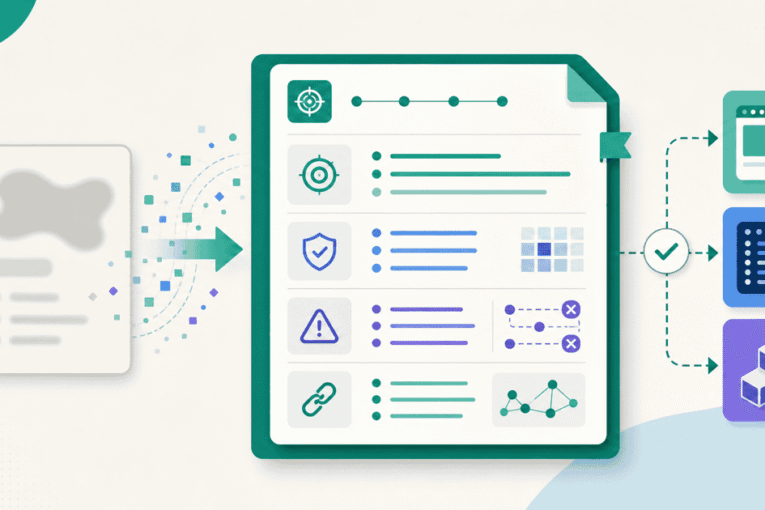
Spec-driven development: how teams define done before AI writes code
Spec driven AI development defines observable behavior, acceptance criteria, invariants, failure cases, proof methods, unresolved decisions, and scope before implementation. The specification…
-
Context Files Can Make Agents Work Harder and Still Miss the Task
A larger instruction file is not automatically a better briefing. Agents need current repository truth selected for the task, with a path…
-
The Dangerous Decision Hidden Inside “Reuse the Existing Component”
“Reuse what exists” sounds safe, but matching names do not prove matching responsibility. Reuse needs search, boundary analysis, and a recorded reason.
-
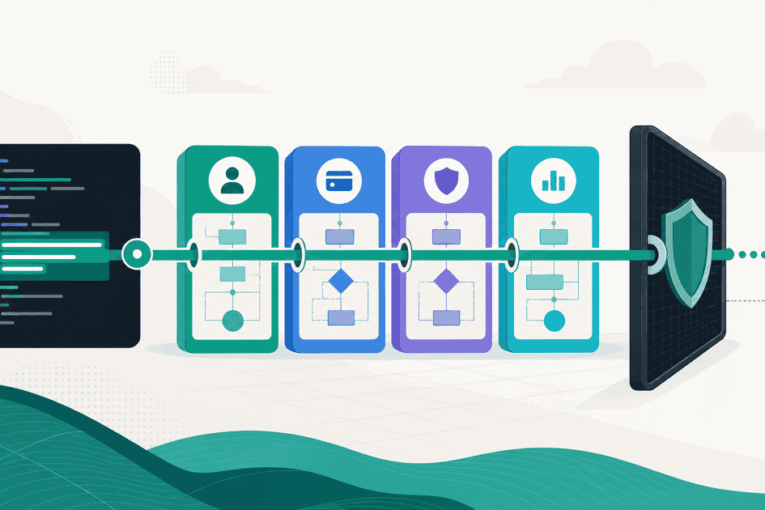
Module attribution: the quiet control that decides which AI rules apply
AI codebase governance starts by attributing every requested and changed surface to owned modules. Module identity selects rules, sensitivity floors, reviewers, checks,…
-
What a Team-Ready AI Plan Must Expose Before Execution
A list of files is not a plan. A useful AI plan reduces the guessing that would otherwise become code, tests, and…
-
What a reviewable AI feature plan must contain before coding starts
AI feature planning is reviewable when it records the requested outcome, module ownership, assumptions, risks, mitigations, reuse evidence, unresolved decisions, implementation steps,…