
TL;DR
Turn an ambiguous ticket into a reviewable AI pull request by settling the intended behaviour before coding, limiting what the agent may change, and attaching proof for every acceptance condition. Pause when the agent finds a product, privacy or architecture decision it cannot own. The reviewer should receive a small diff, the approved requirement, test results, important decisions and known gaps, without a polished summary that hides how the change was made.
In this article
7 min read
An AI coding agent can open a pull request from a ticket. That does not mean the pull request is ready for another engineer’s time.
The difficult part sits between those two events. A short ticket often hides product rules, affected modules, privacy choices and failure behaviour. If the agent quietly decides those points while writing code, the reviewer has to reverse-engineer both the requirement and the implementation from the diff.
That concern appears in real engineering discussions. One team described a flow from Jira ticket to agent implementation and pull request, while reviewers elsewhere reported large AI-generated changes whose authors could not explain them. The useful question is therefore whether each handoff leaves the next person with less uncertainty.
This article uses a fictional account-export feature to show what that looks like. It is a composite example, not a client result.
Start by turning the ticket into a decision
The ticket says: “Add account export.” That sentence does not yet describe a buildable feature.
Before code begins, the team needs to decide who may request an export, which records it includes, what format it uses, how long the file remains available, and what happens when an account has already been deleted. Those are product and privacy decisions. A coding agent can discover the ambiguity and prepare options, but it should not choose the organisation’s policy.
From vague ticket to reviewable handoff
| Weak ticket handoff | Reviewable feature handoff |
|---|---|
| “Add account export” | Named user, trigger and expected outcome |
| Agent infers scope from nearby code | Approved list of included and excluded data |
| Tests follow the implementation | Acceptance conditions exist before the diff |
| Questions appear in review comments | Material questions pause the workflow |
| PR says “tests pass” | PR maps proof and gaps to each condition |
NIST’s AI Risk Management Framework says targeted use and scope should be documented, human oversight should be defined, and a decision should be made about whether development or deployment should proceed. It is broad risk guidance, not a coding workflow. Applied here, it supports a simple boundary: the agent may prepare evidence, while accountable people own material product and risk decisions.
Give the agent a bounded specification
For the fictional export feature, the approved specification might say:
Account-export acceptance conditions
- Only an authenticated account owner may request an export.
- The export contains profile, billing and activity records listed in the data map.
- The job produces one encrypted archive and expires it after 24 hours.
- Repeated requests do not create duplicate background jobs.
- Deleted-account finance records stay excluded until privacy and finance owners decide otherwise.
- Every request and download creates an audit event.
This is more useful than a long design document if every item can be checked. It gives the agent a target, the reviewer a reading order and the tests a reason to exist.
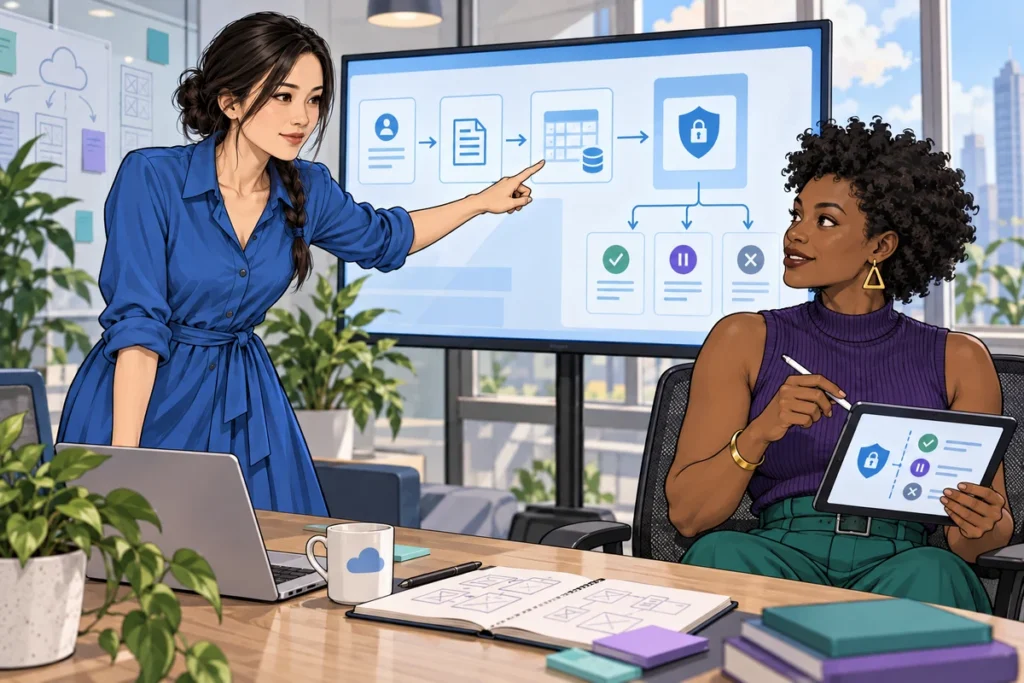
The specification should also name the allowed change surface: the export endpoint, job, storage adapter, tests and documentation. If the agent discovers that the task requires a new retention policy or a shared authentication rewrite, it has crossed the boundary. It should pause with the affected decision, evidence and options.
Make the pause useful to a human
A bad pause asks, “Should I continue?” A useful pause says what changed and what the decision will affect.
In this example, the agent discovers that deleted accounts retain a limited finance record. It prepares three options:
- Include those records, which broadens the privacy and authorization review.
- Exclude them and disclose the limitation in the export manifest.
- Stop the feature until the retention policy is reconciled.
The product and privacy owners choose the second option for this release. The specification changes version. Planned tests based on the old assumption become invalid before they are written.
The pause is part of delivery. It prevents an implementation detail from becoming an accidental product promise.
Build the pull request around the reviewer’s questions
GitHub’s pull-request documentation describes review as examining commits and file changes, then approving, commenting or requesting changes. Its required-status-check guidance also makes an important technical point: required checks must pass for the latest commit, not an earlier version. A trustworthy PR therefore connects current code to current proof.
Build a reviewer route
- Restate the approved behaviour. Link the current specification version and list the acceptance conditions this PR implements.
- Explain the change surface. Name changed modules and why each one belongs in scope.
- Map proof to promises. Pair every acceptance condition with a test, check or manual review result.
- Record human decisions. Include the retention choice, decision owner and resulting constraint.
- Show current check results. Attach results for the latest commit and distinguish automated checks from human judgment.
- Admit the gaps. List what was not tested, what remains out of scope and what would trigger rollback.
The result is a review route. A reviewer can begin with intent, inspect the riskiest files, verify the relevant evidence and decide whether the remaining uncertainty is acceptable. They do not have to read every chat or trust the agent’s confidence.
Keep the evidence receipt smaller than the evidence
The PR description should not become a dump of logs. Keep the raw artifacts available, but summarise them as an evidence receipt.
| Receipt field | What the reviewer should see |
|---|---|
| Requirement | Current specification version and acceptance conditions |
| Scope | Expected files changed and unexpected files explained |
| Deterministic proof | Test, lint, type, security and migration results for the latest commit |
| Human decisions | Owner, choice, date and affected requirement |
| Operational readiness | Logging, alerts, rollback and support impact |
| Known gaps | Untested paths, deferred work and assumptions still in force |
An evidence receipt proves that named checks ran against a named change. It cannot prove that the requirement was wise, that the tests cover every failure, or that a legal interpretation is correct. Our deeper guide to AI code evidence receipts explains that boundary. The article on verifying AI-generated tests helps reviewers ask whether a green test could have caught the defect it claims to cover.
Use one rule to decide whether the PR is ready
Review readiness rule
The pull request is ready for human review when another engineer can understand the intended behaviour, inspect the bounded change, trace proof to each acceptance condition and see the unresolved risks without reconstructing the agent’s conversation.
If that is not true, send the work back to the missing handoff. Do not ask the reviewer to compensate with more patience.
Paqad is relevant when a team wants those handoffs stored in the repository as structured delivery state. Eliyce provides an AI Delivery Programme for teams that want to design and test the workflow around their own repositories, controls and review capacity.
Frequently Asked Questions
How do you take an AI coding task from an ambiguous ticket to a reviewable pull request?
Convert the ticket into approved, testable behaviour before implementation. Limit the files and systems the agent may change, pause when it finds a decision outside its authority, and make the pull request map the current diff to acceptance evidence, human decisions and known gaps.
Can an AI coding agent take a Jira ticket and open a pull request automatically?
Yes, if the agent has access to the tracker, repository and pull-request tooling. Automation of those actions says little about readiness. The workflow still needs a rule for missing requirements, permission boundaries, current checks and a human owner who can reject the result.
What should stop the agent before it starts coding?
Missing acceptance conditions, an unknown decision owner, unclear data handling, a change outside the allowed modules or the absence of a safe way to test and reverse the work should stop execution. These are signs that implementation would hide uncertainty rather than resolve it.
What proof should be attached before a reviewer opens the diff?
Attach the approved requirement, the latest commit identifier, changed-scope summary, results for required checks, evidence for high-risk behaviour and the list of known gaps. Give each item a stable location so a reviewer can verify it without replaying the agent session.
Who owns a product decision the agent discovers during implementation?
The person already accountable for that product surface owns it: often a product owner, privacy owner, security owner or module maintainer. The agent may explain options and consequences. It should not turn the easiest code path into policy.
What should an evidence receipt admit it could not prove?
It should name untested conditions, environmental limits, manual judgments, deferred checks and assumptions inherited from the specification. A clear gap helps the reviewer make a bounded decision; a polished claim of completeness removes that ability.





